AI-Supported Autonomous IT Operations

Security and Compliance Demands Are Growing. Your IT Team Isn’t.

IT Security, regulatory requirements, and evidence obligations are creating more operational work. At the same time, qualified specialists remain scarce, and many security, IAM, and compliance processes still operate separately.

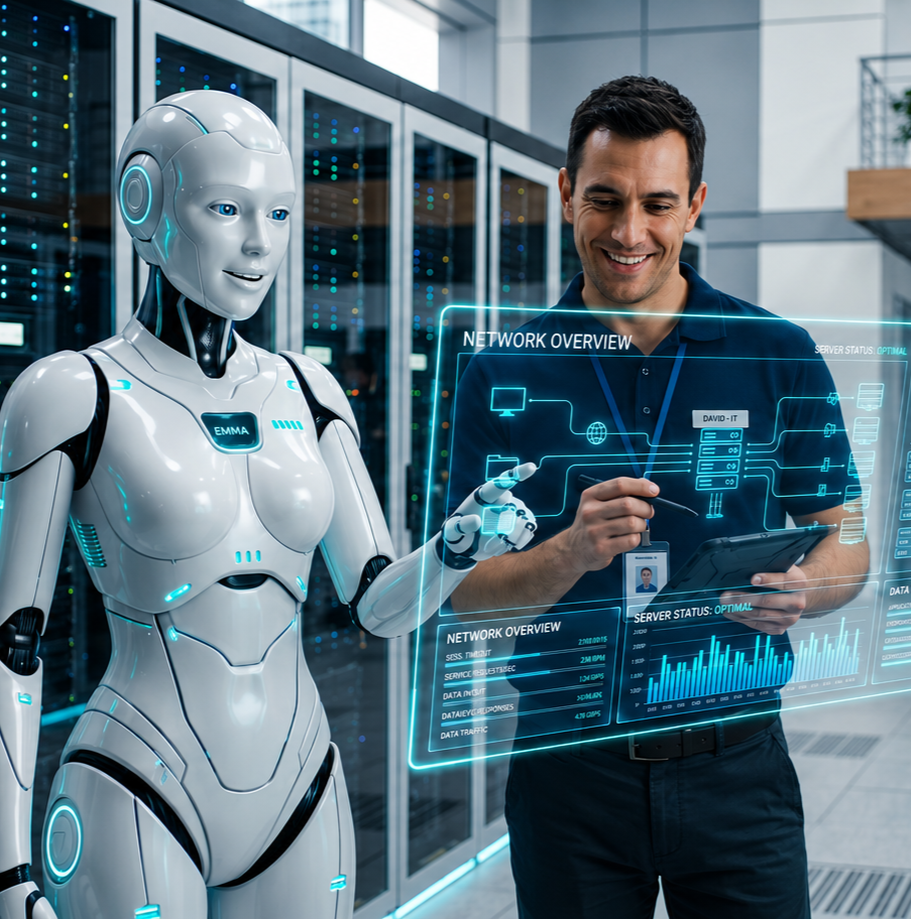
We connect proven core systems with an intelligent AI layer to automate recurring tasks, consolidate information more effectively, and reduce manual effort across security processes in a controlled way.

ChatGPT Image 12. Aug. 2026, 13_02_06-neues-format

More Requirements. More Tools. No More Capacity.  

IT Security and compliance are no longer isolated projects. New regulatory requirements, growing evidence requirements, and increasingly complex system landscapes are placing additional pressure on teams that also have to keep day-to-day IT operations stable.

Staffing Reality

Information security and security operations specialists are hard to find. Additional requirements cannot simply be absorbed by adding more positions.

Structural Reality

SIEM, IAM, ISMS, and other systems each serve important purposes, but they often do not work together as part of one end-to-end process.

Audit Evidence Reality

Audit and regulatory evidence is often compiled manually. When an audit takes place, this creates additional work.
The Core Problem

More Standalone Tools Don’t Solve the Capacity Problem.

New requirements often lead to new tools, additional processes, and more interfaces. Each system can do its job, yet significant manual work remains between monitoring, access management, policy requirements, and actual implementation.

The real issue is the lack of integration across existing systems, information, and processes.

The Shift

From Security Projects to Security Operations. 

Information security and compliance need to become part of day-to-day IT operations rather than recurring add-on tasks.

The goal is an operating model in which security processes, policies, and technical systems are more closely connected. AI can analyze and structure information, while defined automation handles suitable recurring tasks.

Approvals, escalations, and accountability remain clearly defined and traceable. 

Information security that supports IT operations instead of slowing them Down.

What Changes for Your IT Operations

Less Manual Security Work. More Control in Day-to-Day Operations. 

Reduce the Burden on IT

Standardize and automate recurring tasks instead of adding more work to already stretched teams. Experts can focus more on cases that genuinely require assessment and decision-making.

Integrate Compliance Into Day-to-Day Operations

Generate evidence and audit information from existing processes and data sources instead of gathering it manually under time pressure.

Keep Automation Under Control

Define for each process which actions can run automatically, when responsible teams should be notified, and when explicit approval or escalation is required.
The Principle

Connect Existing Systems Instead of Adding Another Siloed Solution. 

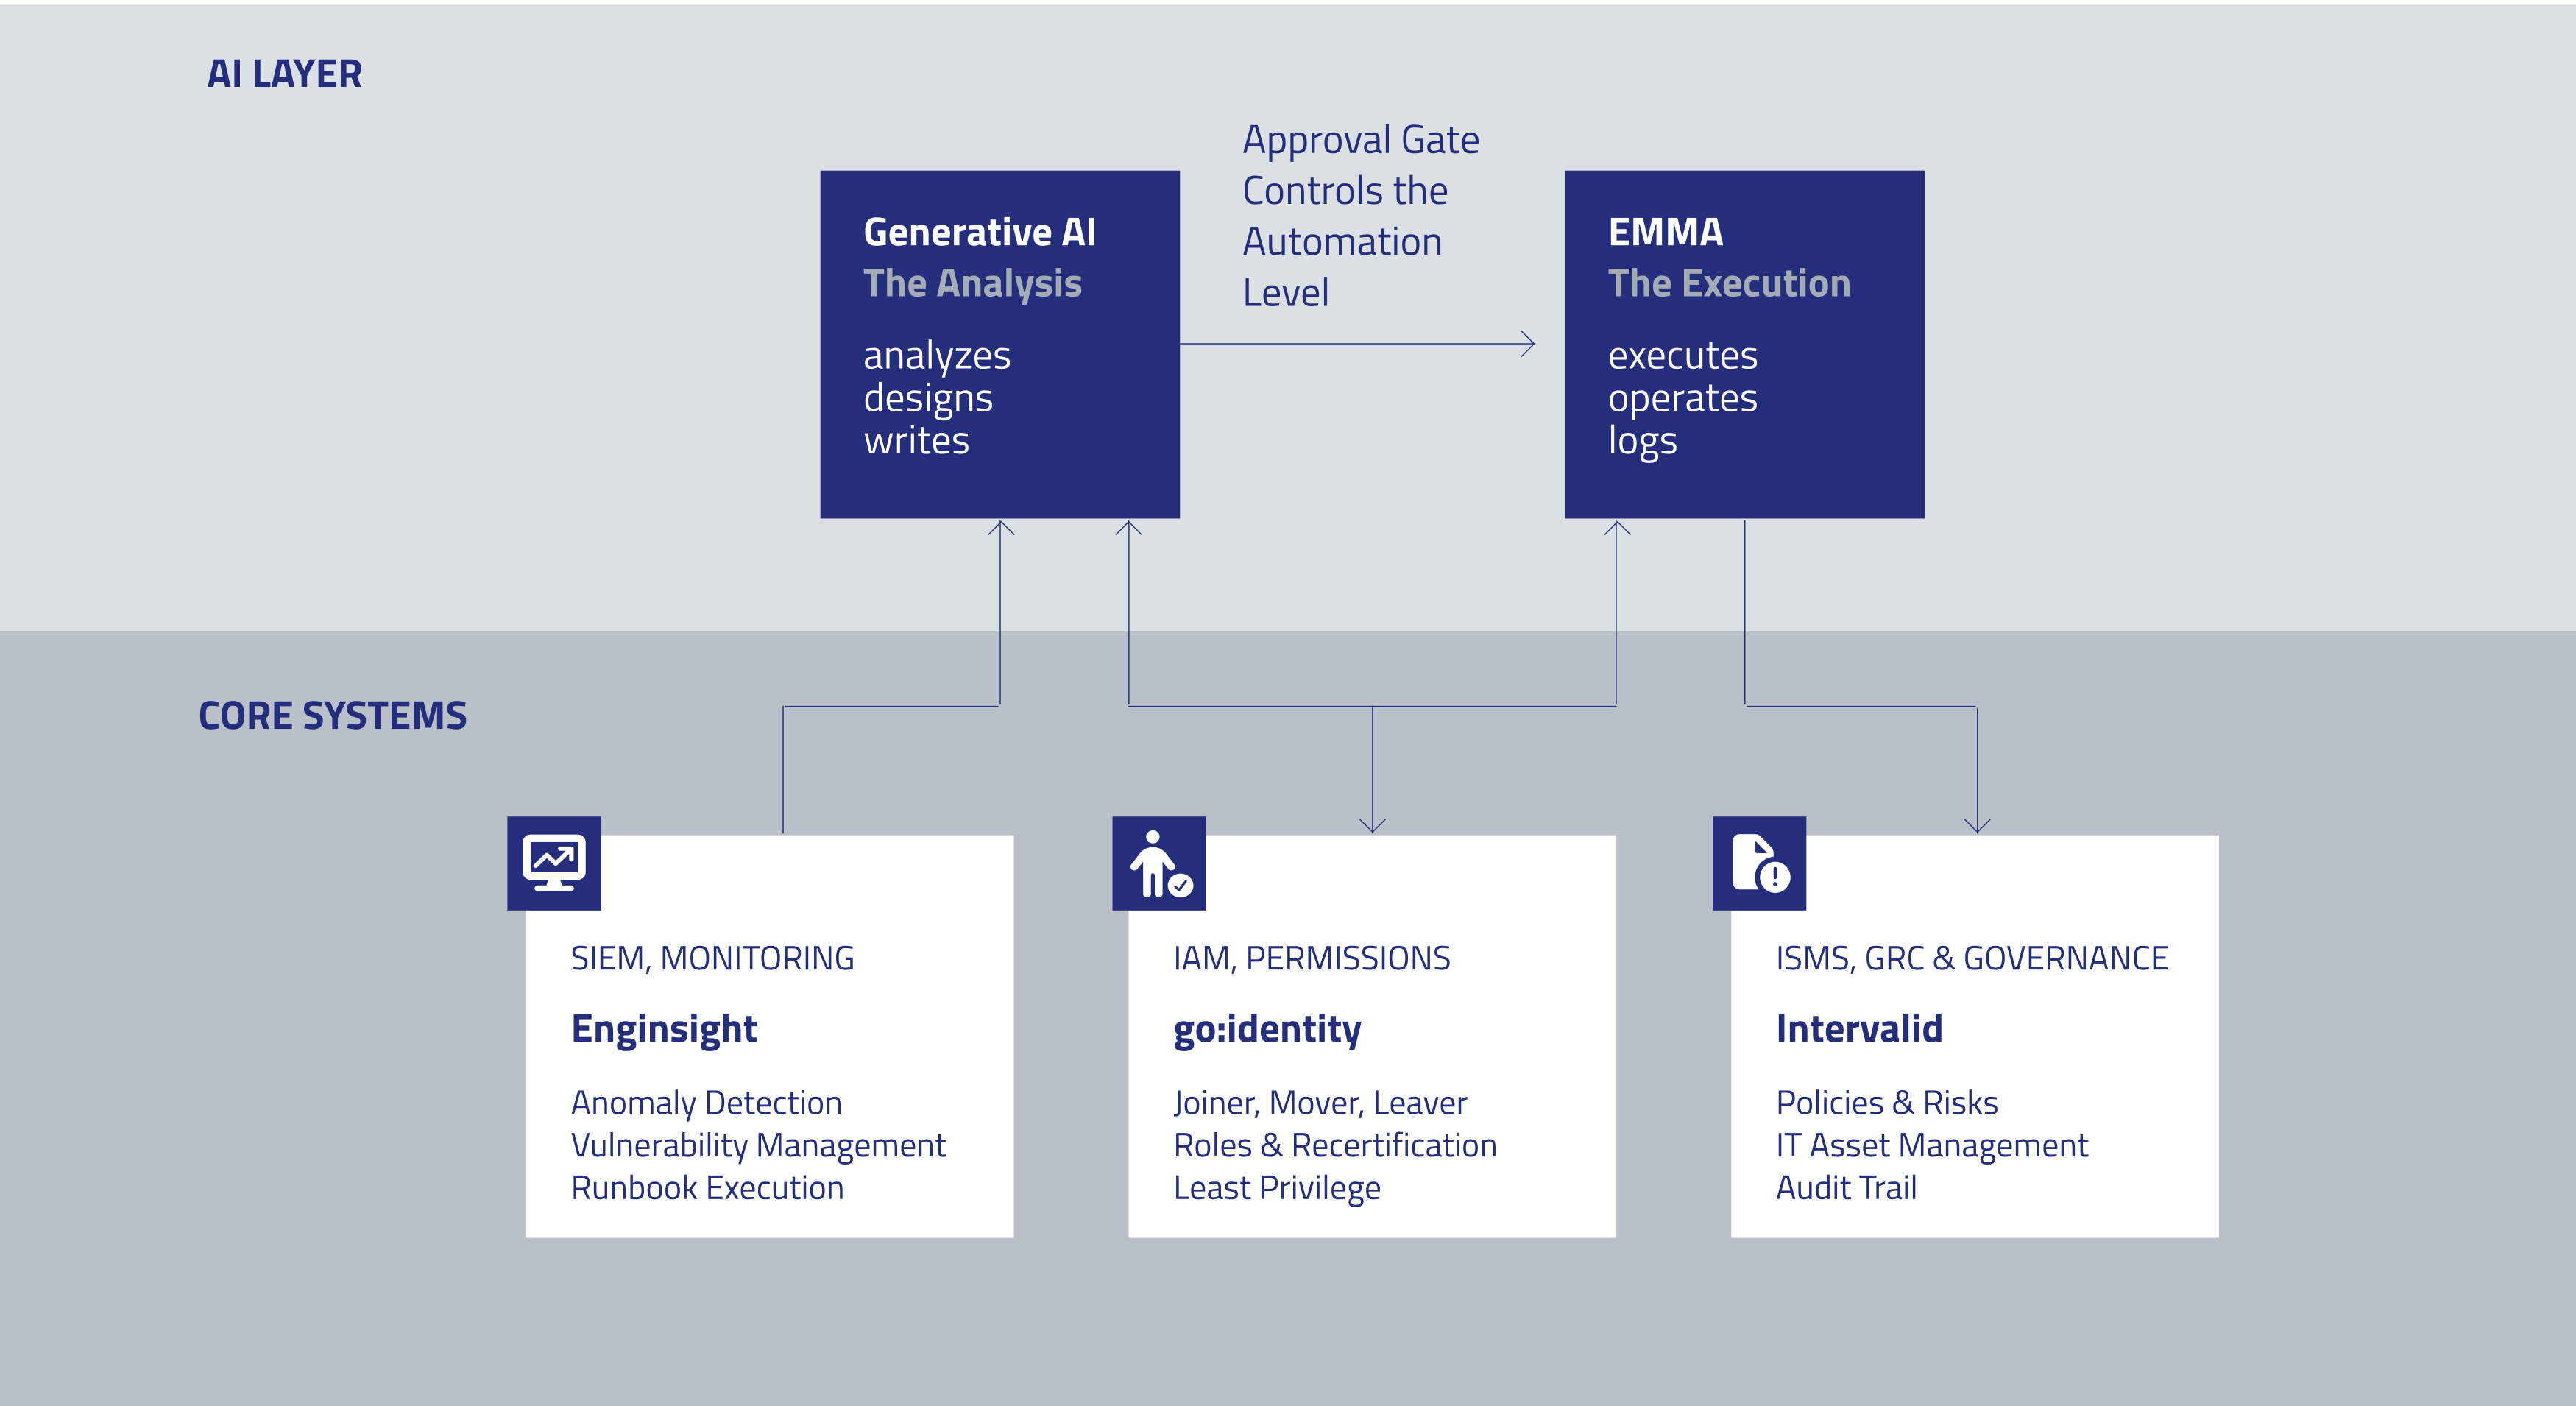
An overarching AI and automation layer can connect analysis and defined execution across existing core systems.

ai-layer-and-core-systems

Existing systems do not necessarily need to be replaced.

What matters is whether they can be integrated effectively into the process and automation logic.

Controlled Automation

Autonomous Does Not Mean Uncontrolled. 

As processes become more automated, clear rules for approval and accountability become even more important. The level of automation can therefore be defined for each process and action rather than through a blanket decision about whether “AI is allowed to act.”

1. Fully Automated

2. Automated with Notification

Runs as planned; IT is notified.

3. Approval

A proposed action is reviewed and approved by a person before execution.

4. Escalation

The case is handed over to the relevant team or executive management for assessment and decision-making.

End-to-End Audit Log: Across all automation levels, the request, timestamp, actor, approval, and execution remain traceable and documented.

The Target State

What Autonomous Security Operations Can Look Like

Autonomous IT operations do not mean that a single system takes over every security task. The target state emerges from several connected areas whose processes can be automated step by step.

autonomous-soc-security-monitoring

Autonomous SOC

Security events are detected, enriched with additional context, and processed according to defined rules. Recurring steps can be automated. People intervene where assessment, approval, or escalation is required.

virtual-ciso-assistant-security-management

Virtual CISO Assistant

Policies, security information, and operational data are brought together to support security leaders with analysis, prioritization, documentation, and strategic oversight.

compliance-dashboard-audit-evidence-1

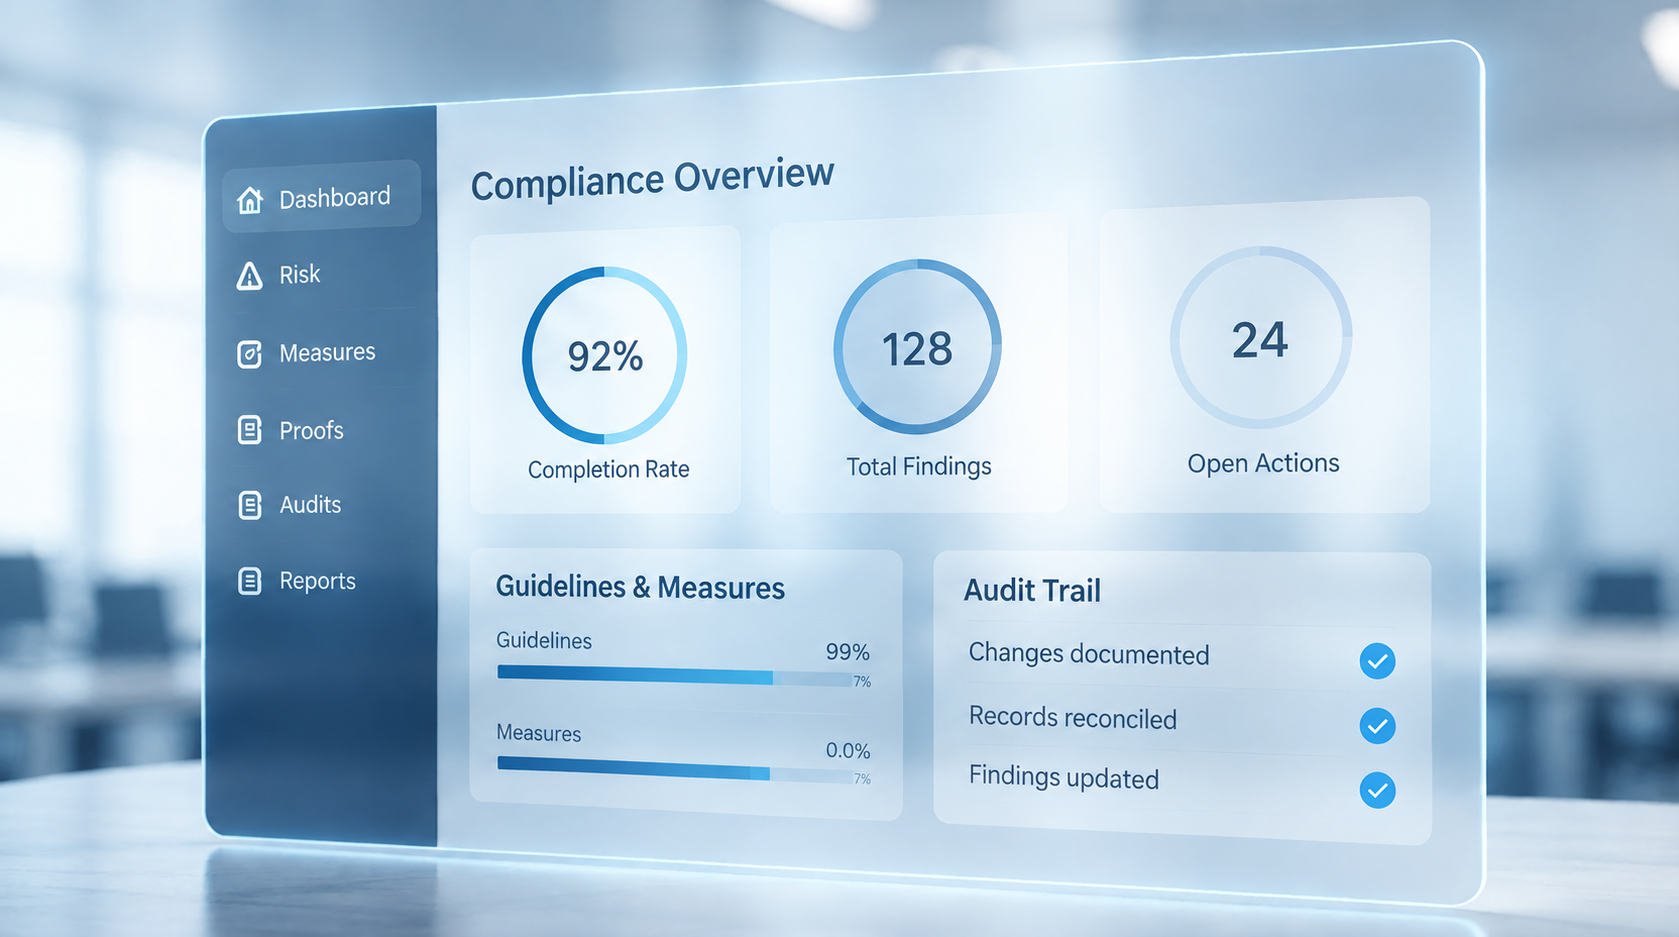
Compliance at the Push of a Button

Evidence is ideally generated where the relevant processes already take place. Recurring evaluations and evidence are produced continuously instead of being assembled manually just before an audit.

None of these building blocks delivers the full value on its own. The value comes from connecting IT Security Operations, governance, and compliance.

In the White Paper

How Does This Become an Operating Model That Works in Practice? 

The basic idea is straightforward: connect systems more closely, automate recurring work, and retain control where it is required. The critical questions lie in implementation.

  • How do you clearly separate analysis from technical execution?
  • How can compliance checks and audit evidence be automated to a greater degree?
  • How do you implement approvals and responsibilities from both a technical and organizational perspective?
  • How does an Autonomous SOC work in a real incident process?
  • How can generative AI and sensitive company data work together in a controlled way?
  • Where can your organization realistically start?
ChatGPT Image 12. Aug. 2026, 13_07_20-neu
No Big Bang

Start Where the Need Is Greatest Today.

The move toward autonomous IT operations does not have to begin with a full-scale transformation program. Each of these steps can deliver value on its own and later become part of a more integrated operating model.

AdobeStock_152598174

Readiness Assessment

Assess the current state and prioritize areas for action.

AdobeStock_152598174

ISMS

Establish a structured framework for policies, risk management, and governance.

AdobeStock_152598174

Technical Audit

Review technical controls and their actual implementation.

AdobeStock_152598174

SOC Pilot

Test automation within a clearly defined scope.

This keeps the broader vision realistic: automate and integrate step by step where there is a clear benefit.

Why ISO-Gruppe?

IT Security Consulting and Technical Implementation Belong Together. 

The real challenge isn’t adding another tool. It’s connecting IT Security requirements, technical systems, and operational processes in a way that creates a viable operating model.

ISO-Gruppe combines IT Security and compliance consulting with technical implementation. Customers can start with individual modules and continue using existing systems. Automation is applied where it can meaningfully reduce operational workload, with defined approvals, traceable processes, and clear accountability. 

  • IT Security & Compliance Consulting
  • Technical Implementation
  • Modular Entry Points
  • Controlled Automation
Frequently Asked Questions

What IT Leaders Need to Know Before Getting Started.

No. The approach is modular and designed to integrate with existing systems. What matters is whether they can be integrated effectively into the relevant process and automation logic.

No. Companies can start from different points—for example, with an initial assessment, an existing ISMS, or an existing monitoring solution.

No. The level of automation is defined for each process and action. Routine tasks can be automated, while critical actions can continue to require human approval or escalation. Decisions and executed steps remain traceable and documented.

Eric Hänsel der ISO-Gruppe

Eric Hänsel
Sales Consultant Security Services

Eichendorffstraße 33
90491 Nürnberg

Germany
Contact

Discuss Your Current Situation With Us.

In an initial conversation, we identify which security and compliance processes currently take the most time for your team and where a practical starting point makes the most sense.

Beispiel

So kann eine zielgruppenspezifische Videobotschaft aussehen: 

Peter-Hildenbrand

Peter Hildenbrand
Director Business Development

Eichendorffstraße 33
90491 Nürnberg

Germany
Kontakt

Mehr Wirkung im Fundraising

Erfahren Sie, wie Sie Videos und Personalisierungen in Ihrem Fundraising einsetzen können. 

Download

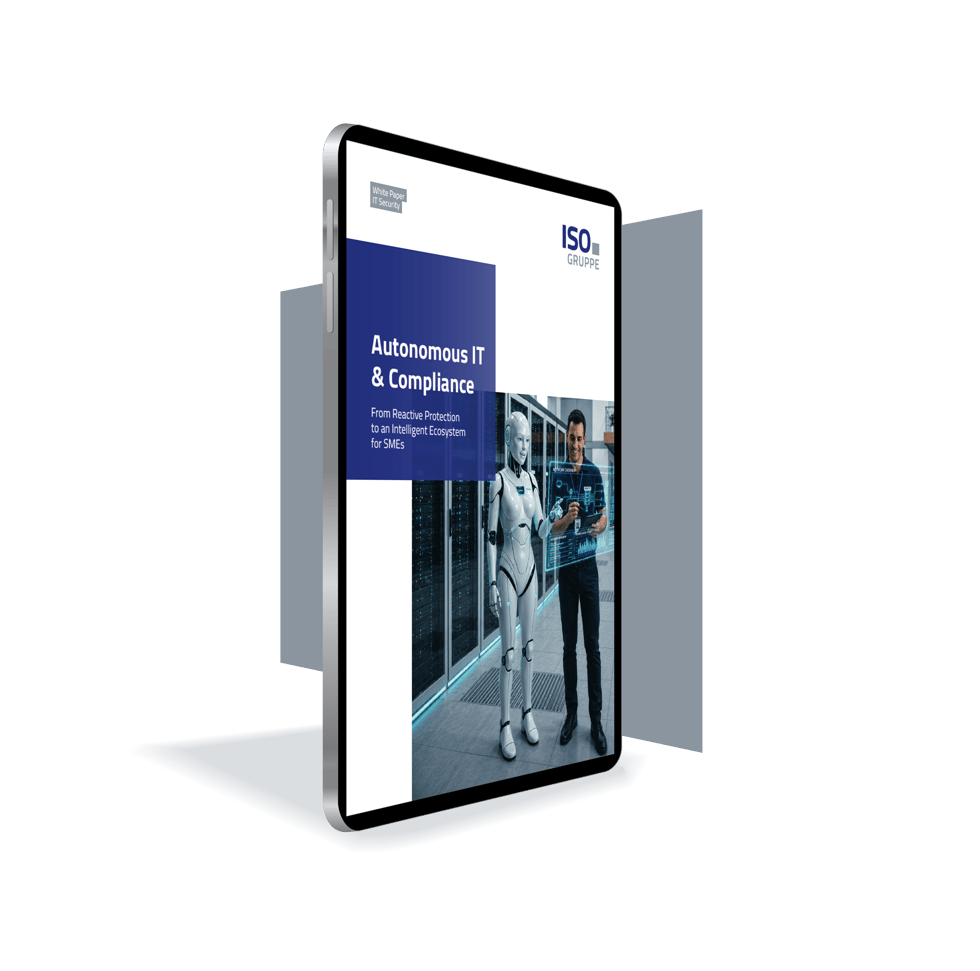
How Can Security Scale Without Expanding Your IT Team at the Same Rate?

The White Paper “Autonomous IT & Compliance” shows how security, compliance, and IT operations can evolve into a shared operating model through integration and controlled automation.

  • Length: 13 pages
  • Audience: IT leaders and CIOs at mid-sized companies 
  • Focus: Autonomous SOC, compliance automation, AI architecture, and modular entry options
EN-Mockup-Autonomous-IT-Compliance